Guide
PCI risk assessment in version 4.0.1: targeted, not generic
PCI risk assessment changed in version 4.0. The old annual enterprise risk assessment gave way to targeted risk analyses, so the question is now which requirements need one and how to record it.
- Not a QSA, stated first
- Introductions to independent QSAs
- Written answers, no call
What changed in PCI risk assessment
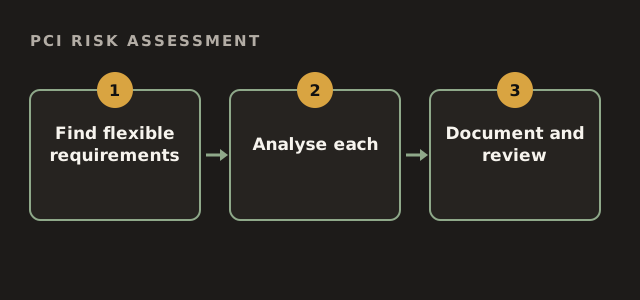
Version 3.2.1 asked for an annual risk assessment. By contrast, version 4.0 introduced targeted risk analyses under requirement 12.3. Therefore you analyse specific requirements rather than writing one broad document. The standard is in the PCI SSC document library.
Where a PCI risk assessment is needed
Some requirements let you set your own frequency. So you must justify that frequency with a targeted analysis.
| Situation | What to document |
|---|---|
| Requirement allows flexible frequency | Why your chosen frequency is enough. |
| Customised approach used | How your control meets the objective. |
| Periodic review | That each analysis was reviewed at least annually. |
PCI risk assessment check
Tick what is in place.
Your result appears here as you tick, so you can see what is still open.
What a good analysis contains
Keep it short and specific. Therefore each analysis names the asset, the threat, the likelihood and the chosen control or frequency.
- The requirement and asset concerned
- Threats and their likelihood
- The chosen frequency or control
- Who approved it and when
PCI risk assessment for small merchants
Merchants on short questionnaires may face few or no targeted analyses. However, check your form, because some requirements still apply. Also, a broader risk view remains good practice.
If you are unsure, list the requirements on your form that mention a frequency. Those are the likely candidates for an analysis.
Where we help
We identify which requirements need analysis and help document them. However, we are not a QSA, so validation remains with you or your assessor.
Also keep analyses in one place with dates and approvers. Assessors ask to see them together, and a single register makes the annual review quick. As a result, the documentation stays current without becoming a burden on the team, even as requirements and systems change.
PCI risk assessment questions
Is the annual PCI risk assessment still required?
Version 4.0 replaced it with targeted risk analyses for specific requirements.
How often are targeted analyses reviewed?
At least once every twelve months.
Do small merchants need a PCI risk assessment?
It depends on the questionnaire, so check which requirements apply.
Can a template help?
Yes, as long as each analysis is specific to your environment.
Related guides
Document your targeted risk analyses
Tell us your form or assessment route. We reply in writing with what needs documenting. Each analysis then has an owner and a review date.
Ask us anything