Insight
PCI compliance credit card over email: what to do when one arrives
PCI compliance credit card over email questions start the same way: a customer sends a full card number in a message. So the real question is how to respond without making things worse.
- Not a QSA, stated first
- Introductions to independent QSAs
- Written answers, no call
Why PCI compliance credit card over email is a problem
Email is not designed to protect card numbers. Messages are copied to servers, backups and phones. Therefore one emailed number can pull several systems into PCI DSS scope.
Also, PCI DSS requires strong cryptography whenever card numbers are sent through messaging tools. Ordinary email rarely meets that bar, so accepting numbers this way creates a gap.
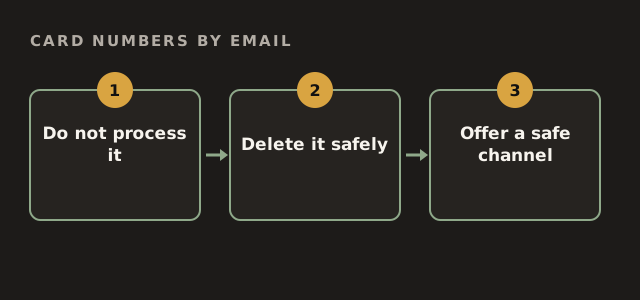
What to do when a card number arrives
Act quickly and consistently. A written routine helps, because staff should not improvise.
- Do not process the payment from the email
- Reply without quoting the card number
- Delete the message, including from deleted items
- Tell the customer how to pay safely
- Record that the routine was followed
PCI compliance credit card over email check
Tick what is true today. Each open item is a quick fix.
Your result appears here as you tick, so you can see what is still open.
Safer channels than PCI compliance credit card over email
The fix is to give customers a better route. For example, a payment link from your provider keeps the number off your systems entirely.
| Channel | Effect on your scope |
|---|---|
| Payment link or hosted page | Card data goes straight to the provider. |
| Phone with secure keypad entry | Agents never hear or see the number. |
| Virtual terminal keyed live | Limited scope, with strict workstation rules. |
Policy and training
Write the routine into your card data policy. Also train staff on it, because inboxes are where the problem appears first. As a result, the response becomes a habit rather than a judgement call.
In addition, tell customers on invoices and order pages that you never accept card numbers by email. So fewer messages arrive in the first place.
Where Winslow helps
We are not a QSA, so we do not assess or certify. However, we write the routine, set up safer channels and prepare you for assessment. Gap analysis and readiness generally run $8,000 to $40,000. The requirement text is in the PCI SSC document library.
PCI compliance credit card over email questions
Is PCI compliance credit card over email ever acceptable?
Only with strong encryption end to end, which ordinary email rarely provides. So most merchants should avoid it.
What if we already processed a card from email?
Delete the message and copies, then fix the routine. Also review whether other numbers sit in old mail.
Does deleting fix PCI compliance credit card over email risk?
It removes the stored copy, but backups and synced devices need checking too.
Should we reply to tell the customer?
Yes, without quoting the number, and offer a safe payment route.
Related guides
Fix PCI compliance credit card over email gaps
Describe how customers pay you today. We reply in writing, usually within one business day, and no phone number is needed.
Ask us anything