Platform guide
AWS PCI compliance: what Amazon covers, and what stays yours
AWS PCI compliance is shared. Amazon states that it is validated as a PCI DSS Level 1 service provider for in-scope services. However, everything you build and configure on top remains your responsibility.
- Not a QSA, stated first
- Introductions to independent QSAs
- Written answers, no call
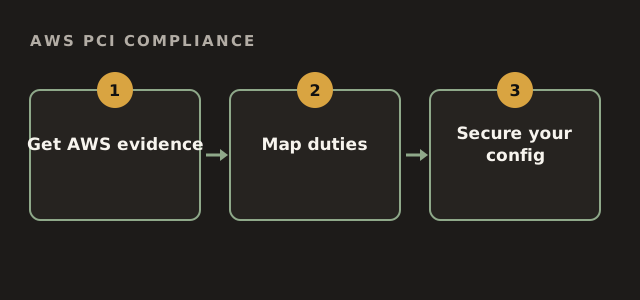
What AWS covers in AWS PCI compliance
AWS covers the physical infrastructure and the services in scope of its assessment. Therefore you can rely on its evidence for that layer. See the AWS PCI DSS FAQs.
What stays yours in AWS PCI compliance
Your configuration is where most findings appear. So focus on these areas.
- Network design and segmentation of the card environment
- IAM users, roles and multi-factor
- Encryption of card data at rest and in transit
- Logging, monitoring and review
- Patching of instances and containers
AWS PCI compliance check
Tick what is in place.
Your result appears here as you tick, so you can see what is still open.
Getting AWS PCI compliance evidence
AWS publishes its PCI attestation and responsibility guidance through AWS Artifact. Also, your assessor will want to see that the services you use are in scope.
| Evidence | Where it comes from |
|---|---|
| AWS attestation | AWS Artifact. |
| Service scope list | AWS compliance pages. |
| Your controls | Your own configuration and records. |
Common AWS PCI compliance mistakes
A frequent mistake is a flat network where card systems share security groups with everything else. Therefore the whole account falls into scope. Another is broad IAM roles, which make access hard to justify.
Separate accounts for the card environment often solve both. As a result, scope shrinks and access becomes easier to explain.
Where we help
We design segmentation, map shared duties and prepare evidence. However, we are not a QSA, and we are not affiliated with AWS. The standard is in the PCI SSC document library.
Also tag resources that belong to the card environment. Tags make scope visible in billing, monitoring and access reviews, so it becomes easier to show an assessor exactly what is in scope and what is not.
AWS PCI compliance questions
Does AWS PCI compliance make our workload compliant?
No. It covers AWS's layer, while your configuration is assessed separately.
Where do we get the AWS attestation?
Through AWS Artifact in your account.
Are all services in scope for AWS PCI compliance?
No, so check the current list before using a service for card data.
Are you affiliated with AWS?
No. We are independent.
Related guides
Design your AWS card environment properly
Tell us your AWS setup. We reply in writing with gaps and a budget range.
Ask us anything