Insight
PCI compliant network design: segment, restrict and document
PCI compliant network design keeps card data in a small, well-guarded part of your network. So the assessment covers fewer systems, and an intruder finds fewer paths.
- Not a QSA, stated first
- Introductions to independent QSAs
- Written answers, no call
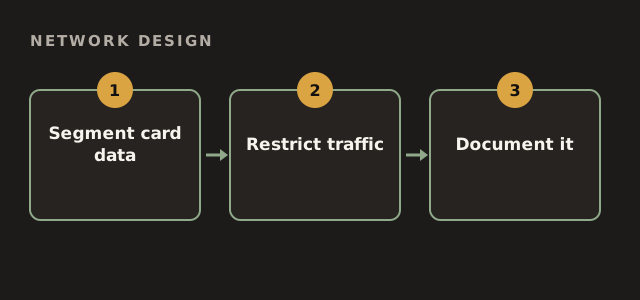
Principles of PCI compliant network design
Good design starts with separation. Systems that handle card data sit apart from everything else. Therefore office laptops, guest Wi-Fi and development servers cannot reach them freely.
Also, traffic is allowed only when there is a business reason. Everything else is denied by default.
Building blocks of PCI compliant network design
The standard calls these network security controls. However, the idea is simple.
| Control | Purpose |
|---|---|
| Segmentation | Separates the cardholder data environment |
| Restricted inbound and outbound traffic | Only necessary connections allowed |
| Wireless isolation | No path from Wi-Fi into card systems |
| Secured admin access | MFA and controlled jump points |
PCI compliant network design check
Tick what is true and documented.
Your result appears here as you tick, so you can see what is still open.
Documentation in PCI compliant network design
PCI DSS expects a current network diagram and a data flow diagram. Also, rules need a documented reason and regular review.
- Network diagram showing all connections to card data
- Data flow diagram for each payment channel
- Rule sets with business justification
- Review records at least every six months
Testing the design
A design is only as good as its proof. Therefore segmentation is tested at least annually for merchants, and after significant changes. Also, rule reviews catch permissions that crept in.
In addition, cloud environments need the same thinking. Security groups and virtual networks play the role of firewalls.
Where Winslow helps
We review designs, diagrams and rule sets before assessment. We are not a QSA. Gap analysis generally runs $8,000 to $40,000, with remediation on top. Requirements are in the PCI SSC document library.
Also involve the people who run the network day to day. Because they know the exceptions, they spot paths that diagrams miss. So reviews become more accurate. In addition, record each approved exception with an owner and an end date, because temporary rules tend to become permanent.
PCI compliant network design questions
Is segmentation required in PCI compliant network design?
It is not mandatory, but without it the whole network falls in scope.
How often should PCI compliant network design be reviewed?
Rule sets at least every six months, and diagrams whenever the network changes.
Does PCI compliant network design apply in the cloud?
Yes. Security groups and virtual networks do the same job.
Who tests segmentation?
A qualified, independent tester, at least annually for merchants.
Related guides
Review your PCI compliant network design
Send a rough description of your network. We reply in writing, usually within one business day.
Ask us anything